 View Upcoming Digital Marketing, Media and Advertising Conferences & Exhibitions
 Phone:
Posts Tagged "First-party Data"


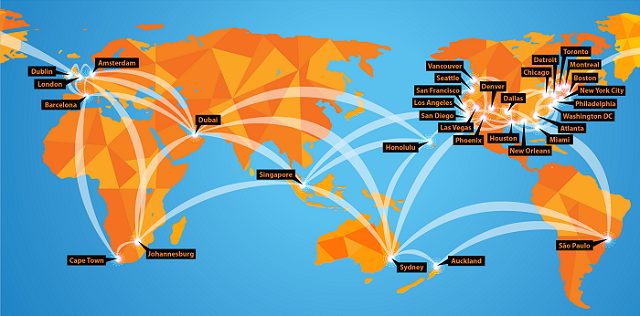
DigiMarCon is the Largest Digital Marketing, Media and Advertising Conference & Exhibition series in the world, with annual events held in all continents (North America, Latin America, Europe, UK, Asia Pacific, Middle East and Africa) in 13 countries (United States, Canada, Australia, New Zealand, United Kingdom, Ireland, Netherlands, Spain, Brazil, Singapore, India, United Arab Emirates and South Africa), across 33 cities (New York, Philadelphia, Boston, Toronto, Vancouver, Montreal, Houston, Dallas, Chicago, Los Angeles, San Francisco, Seattle, Washington DC, New Orleans, Atlanta, Detroit, Miami, Denver, San Diego, Phoenix, Las Vegas, Honolulu, London, Dublin, Amsterdam, Barcelona, Johannesburg, Cape Town, Dubai, Sydney, Auckland, Singapore and Sao Paulo). All DigiMarCon Events can be attended in-person or online. Wherever you are located there is a regional DigiMarCon event nearby you can attend.
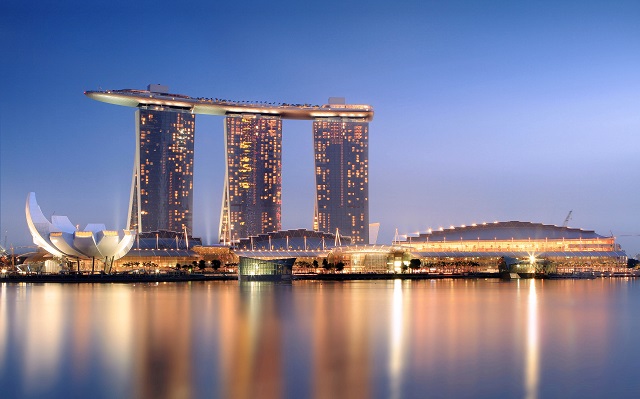
DigiMarCon Conferences are held in top luxury 5-star event venues across the world such as; Royal Caribbean Cruise Ships, Olympic Stadiums, Marina Bay Sands Expo & Convention Centre and Wynn, JW Marriott, Marriott Marquis, Hyatt Regency, InterContinental, The Westin, Renaissance, Hilton, Conrad, W, Sheraton, Loews and Sofitel Hotel properties. Discount hotel room rates at each venue hotel means no hassle getting to and from the venue each day.
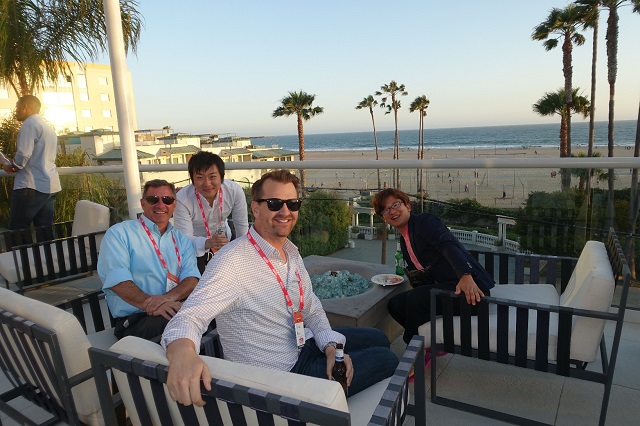
Building relationships matter! At DigiMarCon Conferences we have more networking breaks on our program than others. On average there are 8 Networking breaks at each event giving delegates ample opportunities in a relaxed atmosphere to meet others over the 2-days at the event; from 1-hour round table networking luncheons to 3-hour dinner receptions. These networking breaks are set in picturesque locations to facilitate memorable experiences while fostering new relationships. Such experiences include enjoying cocktails and the Sunset over the Pacific Ocean on a private Ocean Terrace in Santa Monica, to being on the Sydney Olympic Stadium playing arena at night enjoying cocktails under the lights, to dining at the 360 Revolving Restaurant at the top of the CN Tower in Toronto for a Dinner Reception, enjoying cocktails on a private promenade overlooking Times Square in New York City, or having fun at the Dazzles Night Club onboard the Royal Caribbean Oasis of the Seas for a Farewell Party, etc.
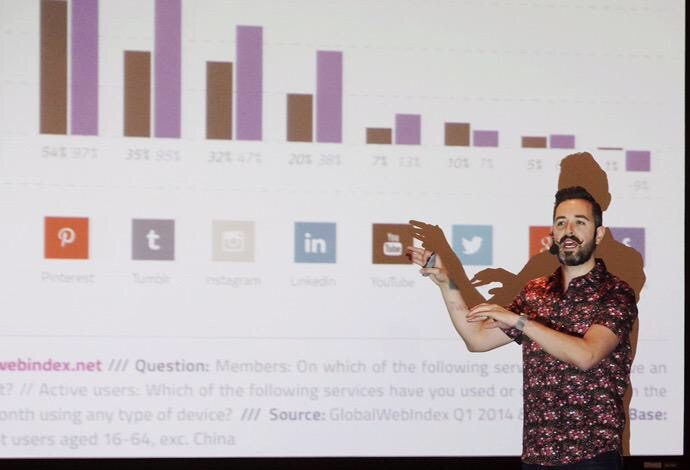
DigiMarCon Keynotes, Panels and Master Classes are facilitated by the foremost thought leaders in the industry, from celebrity social media influencers to CMO’s from the largest Fortune 500 company brands that are disrupting the digital marketing, media and advertising industry, such as Google, Facebook, Microsoft, Amazon, Oracle, Adobe, eBay, Netflix and more. All presentations are pitch-free, and include actionable takeaways, case studies, strategies and tactics, ready to be applied when back in the office.
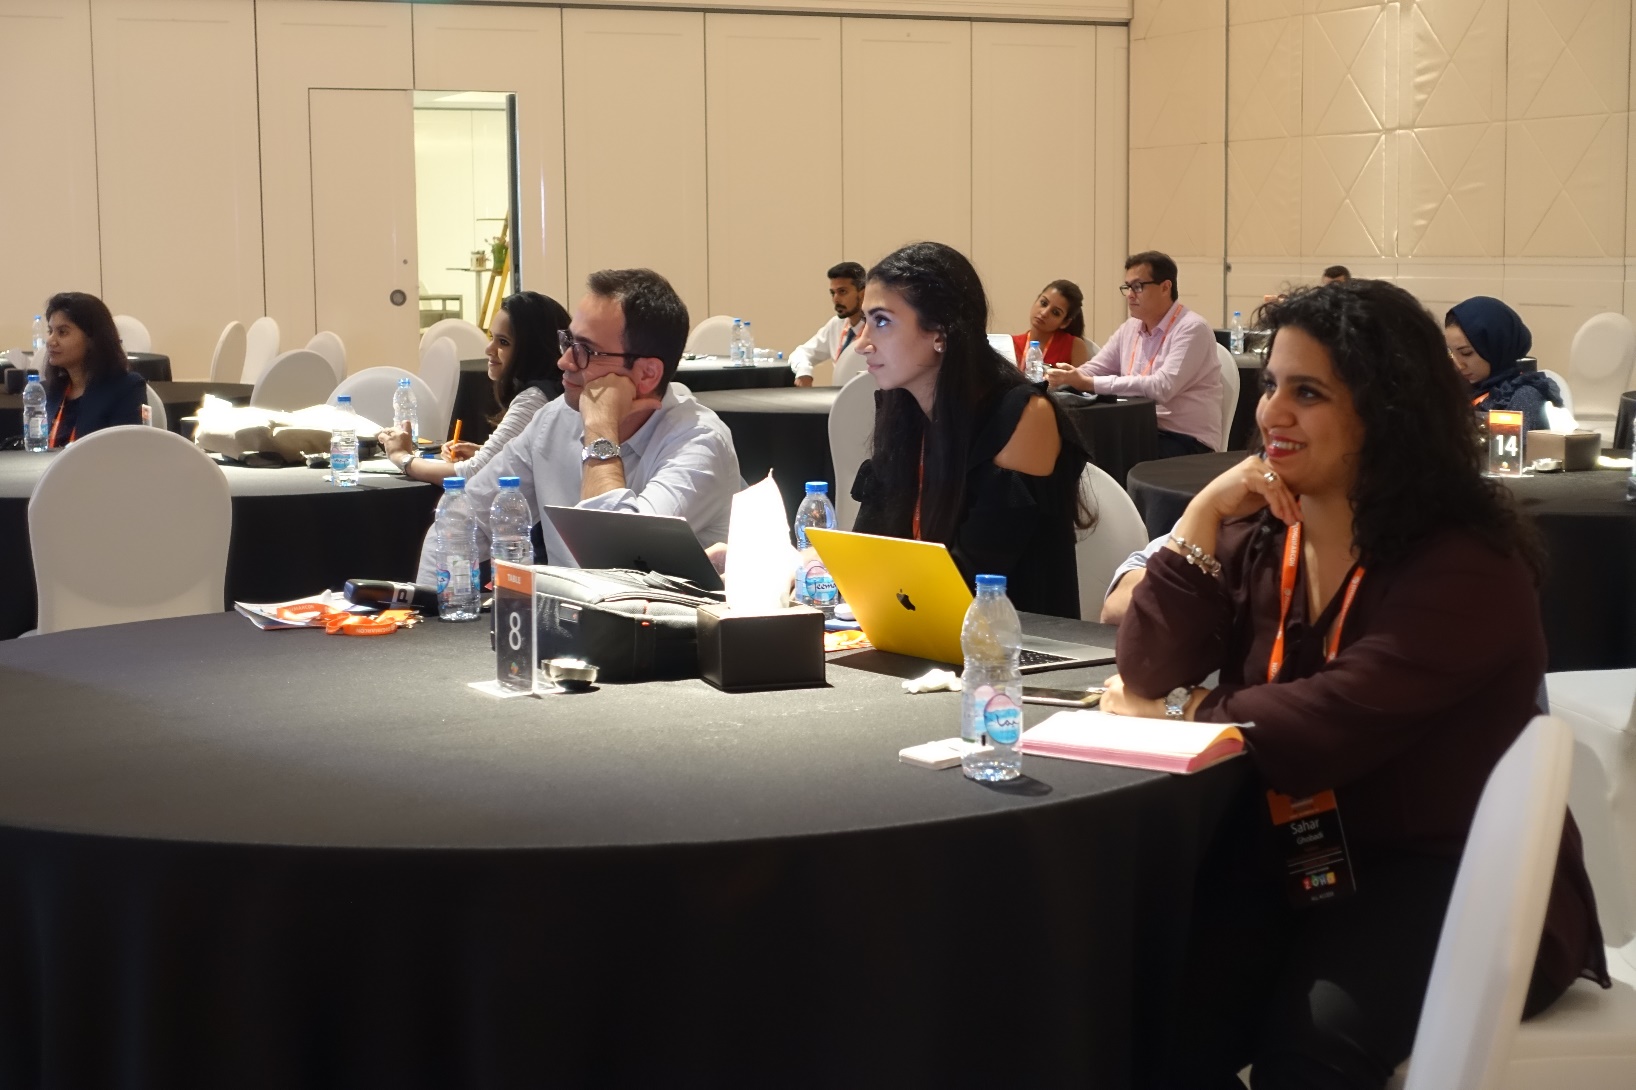
At DigiMarCon Conferences you are never ‘left in the dark’…. literally, in a large room far away from the stage and speakers, crushed in tight theater seating, without even a table, while sitting in the dark. At DigiMarCon all delegates have premium meeting space in luxurious ballroom well-lit spaces, with comfortable seating with table enabling delegates to use their laptop to take notes with ample charging facilities onsite in a comfortable space to learn and thrive. All tables are situated close with direct view of the stage.
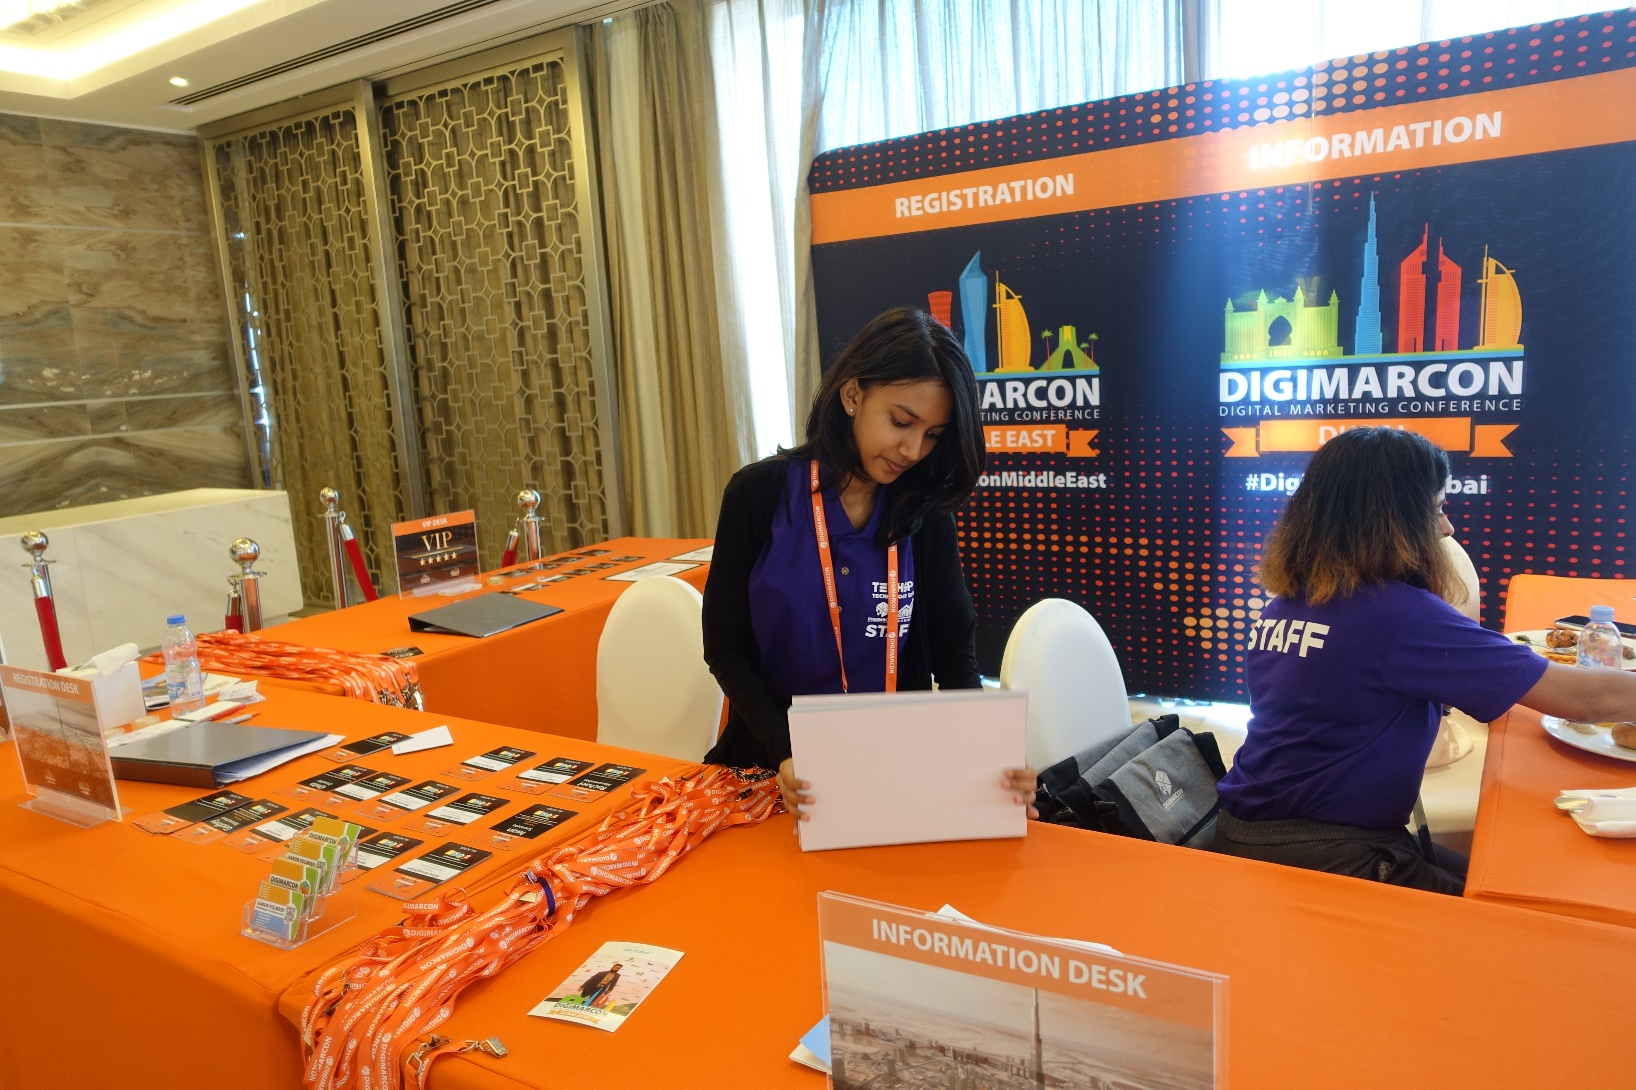
DigiMarCon Conferences are affordable to attend, from single-day event passes up to two-day VIP options at a fraction of the cost of other industry events. We offer significant discounts for early bird registrations. Additionally, on top of time-limited discount pass rates, because budgets are tight, we want to make sure all groups have a chance to attend DigiMarCon. For government employees, students, academic, startups, non-profit organizations and teams, we offer generous discounts off the prevailing registration price.
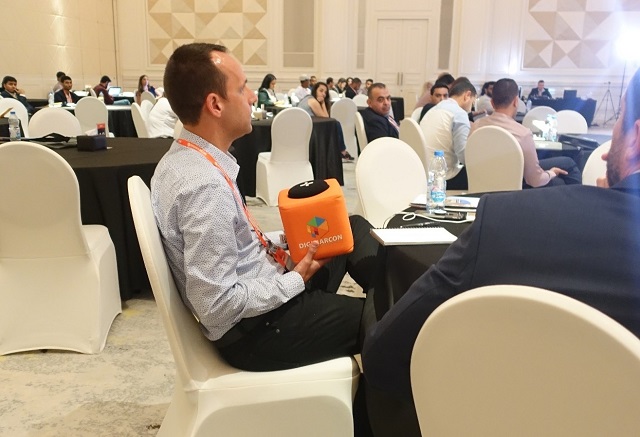
Attend DigiMarCon and you become part of the show! DigiMarCon Conferences tap into the talent of the room, drawing from the knowledge and experience of the professionals in the audience. All DigiMarCon events include regular interactive question and answer sessions with speakers and the audience ideal for collaboration, audience polls, along with ice-breaker and group exercises, steered by charismatic Emcees.
DigiMarCon Conferences put you right up and close with the speakers giving you the opportunity to meet these social media influencers which you follow in person. Speakers are never hidden in private speaker rooms away from the audience, they are in the auditorium sitting right beside you and participating.
Attending a conference is a well-researched decision. There are many factors to consider such as location, time, venue, cost, speakers, content, etc. At DigiMarCon our results-obsessed Customer Service team are at your service before, during and after the event to help with your needs. It’s at the core of what we do — it drives our business. Offsite, we are ready to assist you via phone, ticket or chat. Onsite at our Conferences, friendly DigiMarCon staff serve as your hosts. They welcome your input and are happy to assist you.
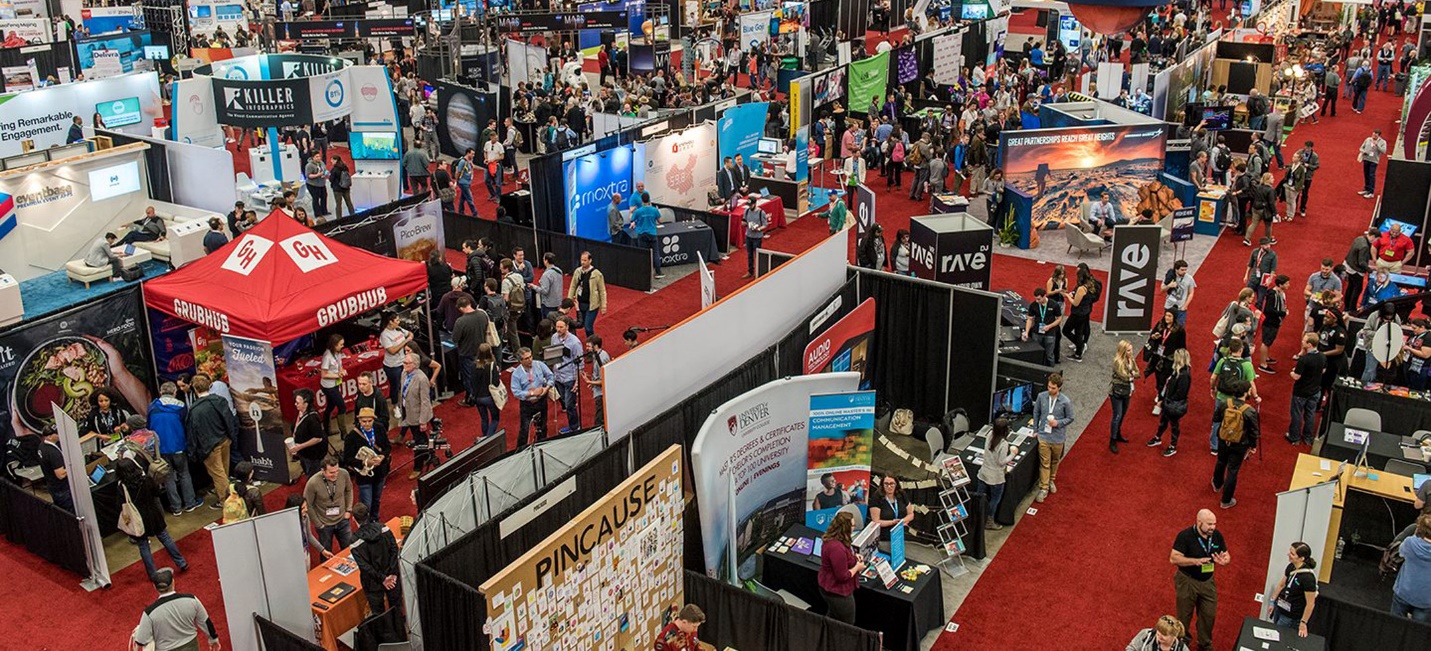
At all DigiMarCon Conferences is the co-located exclusive event TECHSPO Technology Expo, which showcases the new generation of technology and innovation, including; AdTech, MarTech, Internet, Mobile and SaaS technologies. Be inspired, amazed and educated on how these evolving technologies will impact your business for the better. Unlimited Access to TECHSPO Technology Expo is included with all DigiMarCon passes.
DigiMarCon All Access & VIP Passes include a 12-month on demand access to hundreds of hours of DigiMarCon speaker keynotes, panels and master class presentations from recent DigiMarCon Conferences, including videos, slide decks and key takeaways, available on demand so you can watch what you want, when you want.
Attendees of DigiMarcon Conferences gain membership to an exclusive global Digital Marketing, Media and Advertising Community of over 500,000 worldwide subscribers to our award-winning digital marketing blog and over 100,000 members to the International Association of Digital Marketing Professionals (visit https://iadmp.org). This global community comprises of innovators, senior marketers and branders, entrepreneurs, digital executives and professionals, web & mobile strategists, designers and web project managers, business leaders, business developers, agency executives and their teams and anyone else who operates in the digital community who leverage digital, mobile, and social media marketing. We provide updates to the latest whitepapers and industry reports to keep you updated on trends, innovation and best practice digital marketing.
The events industry has forever changed in a world affected by COVID-19. The health and safety of our guests, staff and community is our highest priority and paramount. The team at DigiMarCon is dedicated to ensuring a great experience at our in-person events, and that includes providing a safe, clean and hygienic environment for our delegates. Some of the key areas we have implemented safe and hygienic measures include;
DigiMarCon has always been industry leaders of the Hybrid Event experience for years (a hybrid event combines a "live" in-person event with a "virtual" online component), no one needs to miss out on attending our events. Each DigiMarCon Conference can be attended in-person (with a Main Conference, All Access or VIP Pass) or online (with a Virtual Pass) giving attendees a choice for the experience they want to have. Attending virtually by viewing a Live Stream or On Demand enables participation by people who might be unable to attend physically due to travel or time zone constraints or through a wish to reduce the carbon footprint of the event. If you would like to meet the speakers, network with fellow marketing professionals at refreshment breaks, luncheons and evening receptions, check out the latest Internet, Mobile, AdTech, MarTech and SaaS technologies providers exhibiting then it is highly recommended to attend DigiMarCon in-person. As the largest Digital Marketing, Media and Advertising Conference series with events in 33 international cities worldwide, across 13 countries, there is bound to be a DigiMarCon Event near you to attend in-person if you can.
DigiMarCon Conference Series is the annual gathering of the most powerful brands and senior agency executives in your region. The Sharpest Minds And The Most Influential Decision Makers - Together for Two Days.
Who Attends Our Conferences
Brands • Agencies • Solution & Service Providers • Media Owners • Publishers • Entrepreneurs • Start-Ups • Investors • Government • Corporates • Institutes of Higher Learning


Clean Room Data Collaborations and the Future of Privacy-First Digital Marketing
Clean Room Data Collaborations let organizations analyze shared customer information for marketing insights without handing one another raw customer records. These partnerships help brands and publishers learn from first-party data while keeping access controlled. Privacy-enhancing technology (PET) is a method that reduces the risk of exposing sensitive information while allowing data to be analyzed.
For marketers, the promise is useful insight without routine access to another party’s customer data. But technology alone cannot protect people if the parties allow broad queries, unclear purposes, or risky outputs. Strong rules must guide what enters the environment and what results can leave it.
Organizations of different sizes can take part when they have a clear business need and the right permissions. A small brand may work with a retailer, while a large publisher may compare audience trends with an advertiser. Treat the clean room as one part of a privacy-first data strategy, not a substitute for it.
What Are Clean Room Data Collaborations?
A data clean room is a controlled digital environment where two or more organizations analyze combined data without exposing each other’s underlying records. Each party keeps control of its customer data, while privacy controls limit which data and results others can access.
A data clean room is a digital collaboration space, not a physical room or building. A data center is physical computing infrastructure that stores or processes digital information. Data clean rooms are software environments with rules for collaboration, access, and analysis.
These environments can help organizations answer a shared business question without exchanging customer lists. The parties agree on what data is needed, what analysis is allowed, and which outputs may leave. Those limits shape the collaboration from the start.
Data centers are not clean rooms in this sense. A data center can host software that runs a clean room, but its physical security does not set the privacy rules for a collaboration. The digital environment, its controls, and the parties’ agreement do that work.
Before collaborating, parties should settle three questions:
The answers should be specific enough to guide the setup and later reviews. For example, a permitted audience-overlap result may not allow either party to see which individuals appear in both datasets. A broad promise to “share insights” gives less useful direction.
Before sharing anything, agree on the business question the collaboration must answer.
How Clean Rooms Differ from Data Sharing, CDPs, and DMPs
A clean room is the better fit when two organizations need shared analysis but cannot give each other direct access to customer records. The main difference is whether a partner receives data or only approved results from analysis.
Choose a system based on the task: internal customer activation and cross-company analysis are different jobs. A data clean room can work alongside other tools rather than replacing every platform that holds or organizes data.
Clean Rooms Compared with Direct Data Sharing
Direct data sharing gives a partner access to granular underlying data, often through files or a shared database. That access can support detailed work, but the receiving organization can see records beyond a summary result.
Data collaboration in a clean room takes a different path. Parties run agreed analyses in a controlled environment, without exposing each other’s raw records. The result may be a grouped count or a campaign report, not a copy of the input data.
Clean Rooms Compared with CDPs
A customer data platform (CDP) brings a company’s first-party data together to form a unified customer view. A business can use that view to support its own customer journeys, such as choosing which message to send to a customer.
A clean room serves another purpose: it helps parties analyze data across organizations under agreed controls. It can complement a CDP by letting a company use its own customer view internally and collaborate with a partner separately.
A company may still need a CDP even when it uses a clean room. For example, the CDP may help coordinate its own service messages, while the clean room supports analysis with a retailer or publisher.
Clean Rooms Compared with DMPs
A data management platform (DMP) traditionally organizes audience data for advertising and targeting. DMPs have often worked with second-party and third-party data, rather than building a detailed, lasting view of each customer.
A DMP helps organize or reach an audience; it does not by itself provide the same controlled environment for joint analysis. The distinction matters when a partner needs shared insights but should not receive another party’s granular customer data.
Match the technology to the job: internal customer activation calls for a different tool than cross-company analysis.
How Does a Data Clean Room Work?
A clean room collaboration starts with an agreement about the data, analyses, and outputs each party will permit. The provider of each dataset defines the allowed information and activities, and the parties set shared rules before analysis begins.
Access can be granted for an agreed task and revoked when that permission ends. A practical process has four stages: set rules, bring data into the controlled environment, match and analyze permitted data, then review or activate approved outputs.
Set the Collaboration Rules
Each party agrees which data it will contribute and which uses it will allow. The rules may name permitted analyses, approved users, limits on queries, and the types of results that can leave.
One party may permit campaign measurement but reject audience activation. Another may allow only a defined date range or customer group. Clear limits reduce the chance that a useful question expands into unrelated data use.
Match Only the Data Needed
Parties bring approved data into the controlled environment, where the system can compare records using agreed criteria. A match may rely on a specified identifier, such as an email address that has been prepared in a compatible form.
A match requires the designated field values to correspond exactly under the chosen matching rules. If one party uses a different format or definition, the system may fail to recognize records that refer to the same person.
The clean room does not need every field from either dataset. A campaign analysis may need an exposure record, a conversion event, and an agreed matching field, but not a person’s full profile.
Analyze and Control the Output
After matching, parties can run approved analysis, such as measuring audience overlap or campaign results. Privacy controls can block a result when it is too small or could expose an individual record.
Some collaborations can activate an approved result through a permitted channel. For example, the clean room may help a party define an eligible group, while a separate advertising platform delivers the campaign.
Confirm that the matching fields are compatible before expecting meaningful results.
Privacy Technologies That Protect Collaborative Analysis
A clean room can combine several privacy-enhancing technologies so data remains protected during analysis and in its outputs. No single method solves every risk, so the parties may combine technical safeguards with privacy controls.
The right safeguards depend on the sensitivity of the data and the analysis being run. Encryption, trusted execution environments, secure multiparty computation, aggregation, differential privacy, and synthetic data each offer different protections.
Encryption and Trusted Execution Environments
Encryption changes data into a form that cannot be read without the right key. It can protect information while stored or moving between systems, reducing exposure if someone gains access improperly.
A trusted execution environment (TEE) isolates computation in a protected part of a computer. It helps keep data and code separate from other processes while the analysis runs.
Encryption and a TEE address different points in the process. Encryption protects data in storage or transit, while a TEE helps protect data during a defined computation.
Secure Multiparty Computation
Secure multiparty computation (SMPC) lets parties calculate a joint result without revealing their individual inputs to one another. Each party contributes information to the calculation, while the method limits what others can learn from that input.
For example, parties could calculate an audience overlap without handing each other their full customer lists. The output still needs limits, since a result about a very small group may reveal more than intended.
Differential Privacy and Synthetic Data
Differential privacy adds statistical noise to an output. That noise reduces the chance that someone can link a result to one person, while still allowing useful patterns to appear across a larger group.
Aggregation can also reduce exposure by reporting grouped results rather than individual records. Synthetic data takes another approach: it creates artificial records that can support some forms of testing or analysis.
These methods can be combined, but no technique removes every risk. A method that works for broad audience trends may not suit highly sensitive records or a query about a tiny group.
Choose safeguards that match the disclosure risk of the specific data and question.
U.S. Privacy Laws That Apply to Collaborative Data
U.S. data protection is governed by a patchwork of federal and state laws, not one principal national privacy statute. The rules that apply depend on the people, data, and activities involved in a collaboration.
A clean room does not automatically make a data use lawful. The Federal Trade Commission can act against unfair or deceptive practices, including failures to honor a company’s published privacy promises.
Every state has data-breach notification legislation that may apply when a business handles residents’ personal information. A business may need to follow a state’s rules even without a physical location there.
The Children’s Online Privacy Protection Act (COPPA) covers online collection of personal information from children under 13. It requires privacy notices and verifiable parental consent for covered collection.
Washington’s My Health My Data Act covers consumer health data handled by entities doing business in Washington or controlling or processing that data there. Its scope can include health data beyond the reach of HIPAA.
Illinois also changed its biometric privacy law. A 2024 amendment changed damages from a per-scan amount to a per-person limit. In April 2026, the Seventh Circuit held that the limit applies to all pending cases.
These laws do not apply in the same way to every party or dataset. The parties’ roles, the kinds of information they use, and their activities can change their obligations.
Have counsel assess the specific data flows before a collaboration starts. A technical control cannot replace legal review, and a contract cannot remove duties that apply under law.
Map each participant’s data and legal obligations before authorizing a collaboration.
Marketing Use Cases for Clean Room Partnerships
A retailer and a brand can compare audience overlap before committing to a campaign without exchanging customer lists. That early view can help partners plan around shared or distinct audiences.
Agree on the campaign outcome before looking at the results. Clean room use cases include audience planning, campaign measurement, data enrichment, and activation through a permitted channel.
Audience Overlap and Planning
A brand and a publisher can compare how much their audiences overlap. The result can help the brand decide whether the publisher may reach new people or mostly repeat exposure to existing customers.
Data enrichment can add useful context to a party’s view without handing over a partner’s raw customer data. For example, a brand may learn that its customers overlap with a broad audience group, without seeing the individuals in that group.
Planning can also help partners set a useful reach goal. If most of an audience already sees a brand’s messages, the campaign may need a different group or a different media plan.
Campaign Measurement
A clean room can compare campaign exposure data with conversion or transaction data. That analysis may help estimate reach, frequency, and campaign outcomes across participating datasets.
Reach describes how many people saw an ad, while frequency describes how often they saw it. Measurement can also show whether exposed groups later made a purchase or completed another agreed action.
An association between exposure and conversion does not by itself prove that an ad caused the conversion. Other factors may have influenced the customer, so the result should not be treated as proof of cause.
Activation and Retail Media
A party may activate an approved audience through an agreed advertising channel, without receiving the other party’s row-level data. The channel and permitted purpose should be clear before activation begins.
Retail media partnerships can let a brand and retailer assess how advertising relates to sales. The retailer may bring transaction data, while the brand brings campaign exposure data for controlled analysis.
Agree on the desired outcome before the campaign starts, such as reaching new customers or tracking a defined transaction measure. Decide in advance which campaign outcome will count as evidence of value.
Applications Beyond Advertising
Data clean rooms can support collaboration anywhere organizations need joint analysis without routinely exchanging sensitive records. Outside marketing, parties may work with health, finance, energy, entertainment, travel, or app data.
Highly sensitive health and financial information calls for especially careful governance. A clean room can limit routine exposure, but the parties still need a clear reason and approved use for every dataset.
Common settings include:
Healthcare research may benefit when separate organizations can study a shared question without routinely exchanging identifiable health records. The work still needs limits that fit the data and the research purpose.
Financial firms may use joint analysis to spot activity that looks unusual across separate systems. Utilities may compare demand patterns to plan services, while entertainment companies can study broad audience interests.
Travel partners could examine how customers use services at different stages of a trip. Mobile app teams could compare engagement trends across products without giving one another direct access to every user record.
Start with a narrow, clearly defined research or operational question in highly sensitive sectors.
Data Quality Determines the Value of Shared Insights
Clean room analysis is only as dependable as the accuracy, completeness, and consistency of the data that goes in. Weak inputs can lead to missed matches, misleading audience counts, or poor business decisions.
A practical four-Cs check covers completeness, correctness, consistency, and currency. Data-quality frameworks use different dimensions, so this is a useful checklist, not a universal standard.
Completeness asks whether important fields are filled in. Correctness, or accuracy, asks whether the values reflect what happened. Consistency checks whether fields use the same meanings and formats.
Currency means the data is fresh enough for the question. An old address or purchase record may have been accurate when collected but no longer describe the customer’s current activity.
Missing values can keep records from matching, while duplicates can make one customer appear several times. Inconsistent date formats or product labels can also skew results across organizations.
Stale purchase records can distort a campaign readout. If a retailer’s transaction data stops before the campaign period, the analysis may miss sales that followed exposure.
Parties should agree on field definitions before comparing datasets. A “purchase” may mean an order placed for one party and a completed transaction for another.
Check data definitions and freshness before comparing records across organizations.
Limits, Risks, and What a Clean Room Should Block
A clean room should block any query or output that exposes another party’s identifiable records or violates the agreed purpose. What is blocked depends on the rules, but common limits protect raw data and prevent unapproved use.
Being inside a clean room does not make every activity private or compliant. Poor configuration, weak governance, or re-identification can still expose sensitive information.
Common controls include:
Risky outputs can reveal information even when they do not contain names. A query about a very small group, combined with knowledge outside the environment, may point to a specific person.
Rules must also cover who can run queries and how results leave the environment. A poorly set limit may allow repeated questions that reveal more than any single answer.
Partners should not treat “inside a clean room” as a substitute for privacy rules or legal review. A clean room is a setting for controlled work, not a promise that every use is safe.
Review output controls and query permissions whenever the collaboration’s use changes.
Types of Data Clean Room Models
The key choice is whether collaboration stays within one platform or needs to span partners and data environments. Platform-managed models focus on activity inside a service, while neutral or independent models can support work across a wider set of partners.
Choose a model by where the data and partners need to work together, not by a product name alone. Some cloud-native and federated designs can reduce unnecessary data movement.
Platform-Managed Environments
A platform-managed environment is built around one company’s own services and data. Google Ads Data Hub and Amazon Marketing Cloud are examples of clean room environments tied to major advertising platforms.
A walled garden may suit a team that needs analysis within that platform. It can be less suitable when partners need to combine work across services that do not share the same environment.
Access to a platform’s data and tools can shape which questions are easy to answer. Teams should understand those limits before they build a plan around a single service.
Neutral Third-Party Environments
Independent offerings can support collaboration among parties that use different platforms or cloud systems. Snowflake, AWS Clean Rooms, Decentriq, and LiveRamp are examples of products in this area.
These examples describe models, not recommendations. Each environment can differ in how it connects partners, sets privacy controls, and fits existing data systems.
A broader setting may help when a retailer, brand, and publisher need to work across separate environments. The parties still need compatible data and clear agreements about permitted use.
Cloud-Native and Federated Approaches
Cloud-native designs use cloud services to support data processing and collaboration. Federated approaches can let analysis run across separate data environments, which may reduce the need to move every dataset into one place.
Less data movement can lower some exposure risks, but it does not settle questions about access or outputs. The parties still need controls for queries and results.
Cross-partner work may call for broader interoperability than a single platform provides. Check where each participant’s data resides before choosing a model.
How to Evaluate and Launch a Clean Room Collaboration
Begin with one business question that can be answered using data each party is authorized to contribute. A narrow pilot helps teams test whether the analysis can inform a real decision.
Do not launch until the parties agree on permitted use and can prepare compatible data. Marketing, IT, data, privacy, and legal teams need clear roles before the work starts.
Define the Business Question
Write a question that names the decision the collaboration should support. A question such as “Which campaign reached new customers?” gives the team more direction than a broad goal to find insights.
Use this five-part checklist to assess a first collaboration:
Agree on Governance and Partner Roles
Marketing teams can define the campaign question, while data teams prepare and explain the records. IT teams can plan system connections, and privacy and legal teams can review limits and duties.
Set a clear owner for approving queries and outputs. Partners should also agree who can change the permitted purpose and how they will respond if a concern comes up.
A clean room is a poor fit when parties cannot agree on allowed use. It may also fail when their data cannot be prepared in a compatible form.
Test the Data and Measure the Result
Before a full launch, test a small set of records and check whether the matching fields work as expected. Confirm that the planned output answers the business question without exposing records.
Clean room implementation can require data preparation, partner coordination, governance, and links to existing systems. Those tasks need time from several teams, not only the group that owns the campaign.
Measure the pilot against the decision it was meant to support. Pilot one bounded collaboration and keep it only if the resulting insight changes a real decision.
What Comes Next for Privacy-First Data Collaboration
The next stage of data collaboration will depend on connecting more partners and analytical workloads while preserving meaningful controls. Interoperability could help teams work across environments, while more dynamic analysis may support changing business questions.
New methods still need to prove that their outputs are useful and safe for each task. Privacy-enhancing technologies are also being used in work on AI and model development.
Interoperability means systems can work together under shared rules. It may help parties connect data clean rooms that use different tools, though the parties still need agreement on data and output controls.
The IAB Data Clean Room Standards effort is an example of work toward common practices. Standards may make some collaborations easier to plan, but they do not replace choices about data use or privacy controls.
AI and model development can also use controlled collaboration. Parties may want to test patterns across data without giving one another direct access to all of their records.
Synthetic data is another area of development. AWS Clean Rooms supports synthetic dataset generation, which can help teams create artificial records for some analysis tasks.
Synthetic data has a tradeoff: it must remain useful for analysis without resembling source records too closely. If it differs too much, results may not reflect real data; if it stays too close, it may increase re-identification risk.
Build for interoperability, but verify privacy and analytical usefulness in each specific use case.
Conclusion
Clean rooms can make cross-company analysis more practical, but they work best when control and purpose are clear from the start. They let parties study data together without routinely exposing raw records, while privacy still depends on rules, data quality, and governance.
The first step is not choosing a platform. Choose one authorized business question, then align the teams responsible for its data and use.
Write down one collaboration question, identify the data and permissions it needs, and decide which teams must approve a small pilot.
Own Your Audience: The Business Case for First-Party Data and Privacy Architecture
Ever thought if your brand really knows its customers? Or are you just making guesses from digital clues? Most companies have valuable insights locked away in CRM platforms, email systems, or mobile apps.
This makes it hard for teams to understand their audience fully. Without a unified plan, you can’t turn these clues into real revenue growth.
To win today, businesses need a strong first-party data and privacy architecture. It’s not just a plus; it’s a must for keeping customer trust.
True ownership of your audience means more than just collecting data. It’s about smart management, top-notch security, and using data everywhere. By putting all your data in one place, you can make quicker, smarter choices. These choices respect user privacy while boosting your results. Let’s dive into how to make your customer relationships your most valuable asset.
Why First-Party Data Is Becoming a Strategic Business Asset
First-party data has grown from a simple marketing tool to a key part of business strategy. Companies now see direct data as more reliable than data from outside sources. This change shows a move from seeing data as a short-term tool to a durable business asset.
The shift away from third-party identifiers
Digital ads used to rely on third-party cookies and guessed audience segments. These methods gave a broken view of users, leading to bad experiences. Now, businesses focus on permanent identifiers like verified emails and unique IDs.
Switching from short-lived tracking methods gives a clearer view of the audience. This move also cuts down on relying on platforms that change their privacy rules often. Using your own data keeps your insights steady, even when the digital world changes.
Why direct customer relationships improve business resilience
Direct customer relationships act as a strong barrier that rivals can’t easily cross. When you own the history of your interactions, you have a unique story that’s yours. This knowledge helps you stay strong, even when the market is shaky.
Creating these bonds builds lasting loyalty and trust. When customers feel seen at every touchpoint, they stick around. This loyalty is key for growing in a crowded, privacy-focused market.
How owned data supports better decisions across the organization
Owned data is the base for smarter business resilience and planning. By mixing behavioral, transactional, and CRM data, leaders can make more accurate forecasts. This full view helps teams set goals based on real customer actions, not guesses.
Also, this data lets teams offer highly relevant personalization on a big scale. Whether it’s improving products or streamlining supply chains, insights from your own data are priceless. A strong data strategy turns raw data into a clear path to success.
The Business Costs of Relying on Other Companies’ Audiences
Using third-party platforms seems easy but hides big risks. Brands that rely on others to reach their market are just renting their growth. This makes their success shaky, as changes in platform rules can hurt them a lot.
Platform dependency and changing access rules
Digital marketing today is ruled by big platforms. Relying on these systems means you face sudden changes in access rules. This can block your way to reach your audience.
Platform dependency means you must follow rules you didn’t make. If a platform changes its rules, your marketing plans might fail. This makes planning for the future hard and risky.
Unreliable audience signals and incomplete customer profiles
Third-party data quality is often bad. Privacy updates often remove key tracking details. This makes incomplete customer profiles that don’t show what users really do.
Bad data makes it hard to connect with customers. You might target wrong people or not know who’s seeing your ads. This leads to wasted impressions and lost chances.
The financial impact of poor-quality or inaccessible data
The cost of using rented audiences is high. Bad data means you spend too much on the wrong people or on stopping current customers. This financial drain hurts your marketing return on investment fast.
Also, not owning your data means you can’t share insights easily. Investing in audience ownership is key to keeping your data valuable for your business.
First-Party Data and Privacy Architecture
A good privacy architecture ties together all data stages, from start to end. It’s like a blueprint for handling digital info. It combines policies, tech, and controls to manage how we interact with people.
What first-party data and privacy architecture means in practice
First-party data is info gathered directly from people through your own means. It’s different from zero-party data, which users share willingly, or third-party data, bought from others. Effective strategies mix what people do with what they say to understand them fully.
Privacy architecture is the system that keeps this data safe and organized. It makes sure each piece of info follows strict rules. This way, companies avoid messy data silos.
Connecting data collection, consent, security, and responsible use
A modern architecture links different processes into one system. It connects consent management and identity resolution, respecting user wishes at every point. Adding security from the start reduces the risk of unauthorized access.
Responsible use means data is only used for its stated purpose. This makes the tech used ethical. Consistency across these areas is what sets leaders apart from followers.
Why privacy architecture belongs in business strategy
Privacy architecture is key to a business strategy, not just IT. Customer trust is crucial in the digital world, and a secure base is essential. Prioritizing privacy boosts data quality and marketing results.
Aligning data governance with business goals makes companies strong against changing rules. Investing in this architecture lowers legal risks and unlocks deeper insights. A privacy-first approach turns compliance into a growth driver.
Building a First-Party Data Foundation Customers Can Trust
Effective data protection strategies begin with how you invite customers into your digital world. Brands that are open about data collection turn it into a team effort. This makes users feel like they’re working together, not just being watched.
Defining legitimate sources of customer data
Start with places where customers naturally interact with your brand. This includes direct sales, joining loyalty programs, and reaching out for help. These moments give you high-quality signals that are both accurate and given willingly.
Surveys and feedback loops are also great for getting insights without being intrusive. By using your own channels, your data protection strategies meet user expectations. This approach avoids the problems of third-party tracking and gives you a cleaner, more useful database.
Designing transparent value exchanges for data sharing
Customers are more likely to share data if they see the benefits. A clear value exchange shows them what they get in return, like special deals or content. When the deal is fair and clear, more people agree to share their data.
Don’t hide the reason for collecting data in legal terms. Use simple language to explain how it helps them. This builds trust and makes it easier for users to agree to data requests.
Using consent and preference management to preserve choice
Keeping customer choice is key to a trustworthy system. Strong preference centers let users control what data they share and how it’s used. This is a key part of modern data protection strategies.
Think about using progressive profiling to add to your customer records gradually. Instead of asking for a lot of info at once, ask for small pieces as you get to know them better. This approach lowers form abandonment and keeps your data relevant and correct without overwhelming users.
Key Components of a Privacy-Centered Data Architecture
Effective online privacy measures need a solid technical base. This base handles data from start to finish. It keeps performance high and trust with users strong. This way, every interaction is safe, and insights are gained for better engagement.
Data collection and identity resolution layers
The start of a strong architecture is how data is gathered and tied to users. Companies must use systems for deterministic and probabilistic identity to build complete customer profiles. These profiles help in giving consistent experiences and keeping data accurate.
Storage, processing, and access-control systems
Safe storage and processing are key for keeping sensitive info secure. Data that’s up-to-date is crucial for quick, AI-driven decisions and personalizing experiences in real-time. For fast environments, data needs to be processed quickly to keep experiences fresh.
Access controls must be strict to avoid data leaks. By limiting who can see or change data, companies lower their risk. These controls protect data, letting only approved people work with it.
Consent, preference, and purpose-limitation controls
Adding consent records into data flow is essential for following online privacy measures. Controls that limit data use ensure it’s only for agreed-upon reasons. This openness helps build trust and loyalty over time.
Lastly, closed-loop attribution lets companies give feedback to customer profiles. This loop helps improve strategies without losing sight of privacy. By linking these parts, businesses can meet both efficiency and data protection goals.
Turning Customer Data Into Business Value Without Overreaching
Turning customer data into useful business insights is a fine line. It’s about using data to help without invading privacy. Companies must learn to use data wisely to offer value without overdoing it.
By focusing on what matters and keeping things simple, businesses can build trust. This approach also helps them succeed in the market.
Improving segmentation and customer journey analysis
Understanding how customers interact with your brand is key. Analyzing their actions helps create accurate audience segments. This way, businesses can meet specific needs at the right time.
Looking at customer journeys shows where they might get stuck. Using first-party data, businesses can see how users feel. This helps make every interaction better, not worse.
Supporting relevant personalization across owned channels
Personalization means sending the right message at the right time. Brands should use their own data for this. Frequency control is crucial to avoid overwhelming users.
Respecting user boundaries is key. For example, not showing ads for things already bought. This makes the brand experience better and saves money.
Using first-party data to strengthen retention and customer lifetime value
First-party data is vital for keeping customers loyal. Brands like Adidas show how unified data can create strong connections. They focus on nurturing relationships with personalized offers.
When customers feel understood, they come back. This builds loyalty and increases value. By being relevant and transparent, businesses can thrive ethically.
Data Privacy Solutions That Strengthen Information Security
Keeping sensitive data safe is now a key part of information security. Companies need to use data privacy solutions that keep data safe but let teams use it right. This way, businesses can build trust and follow rules in a world full of regulations.
Protecting sensitive information throughout its lifecycle
Data security is important from the start to the end. It means keeping data safe when it’s moving and when it’s not. Lifecycle protection keeps data safe from people who shouldn’t see it, no matter where it is.
Applying encryption, tokenization, and pseudonymization appropriately
Companies should use special methods to hide who data belongs to. Encryption keeps data safe when it’s not moving. Tokenization and pseudonymization make it hard to see who data is about in daily work. But remember, hashing is not enough on its own.
Managing internal access with least-privilege principles
Good information security needs strict rules for who can see what. Least-privilege principles mean people only see data they need for their job. This, along with watching data closely and keeping duties separate, makes sure customer data is treated with care.
By focusing on these data privacy solutions, companies can find a balance. They can get useful insights while keeping user privacy safe. Taking a strong security stance not only lowers risk but also makes customer data more valuable in the long run.
Data Governance Best Practices for User Data Management
Turning raw data into a valuable asset needs careful management and clear roles. Many think they just need to collect more data. But, they often have a data delivery problem. Important data often goes unused, not reaching the systems that need it.
Good user data management keeps your data reliable and useful. By following data governance best practices, companies can make the most of their data.
Assigning ownership and accountability for critical data
Good governance starts with clear roles in your team. Marketing, tech, legal, security, sales, and customer service must all take accountability for their data.
When teams own their data, decisions are quicker and better. This stops the problem of data being stuck in silos, which slows down teamwork.
Creating consistent standards for data quality and retention
Data needs to be checked right when it comes in. Teams should use automated tools for deduplication and keeping data fresh. This makes sure data stays up-to-date and correct.
It’s also key to have clear rules for how long to keep data. Getting rid of old data saves money and reduces security risks.
Maintaining inventories, classifications, and data lineage
Keeping a detailed list of all data is crucial. Proper classification helps spot sensitive data that needs extra protection.
Knowing where data comes from is key. It lets your team check data’s history, helping with both rules and strategic confidence.
Designing a Digital Privacy Framework for Compliance
Companies need to make privacy rules real and followable. A solid digital privacy framework is key for handling user data right. By seeing compliance as a regular part of doing business, companies can earn and keep customer trust.
Connecting privacy requirements to operational controls
Good governance means turning legal rules into real actions. This includes using systems for consent, clear privacy notices, and strict use rules. Consistency is key to make sure data use matches what users agree to.
Putting these controls in campaign tools helps stop wrong data use. This way, every bit of data stays where it’s supposed to. It makes following rules a normal part of business, not just a fix-it job.
Preparing for consumer rights requests and data access obligations
Today, people have more say over their data. A strong privacy compliance framework needs easy ways to handle data requests. Companies should also make it easy for users to say no to data use.
These steps must be quick and reliable to meet legal deadlines and keep customers happy. Automating these tasks helps teams less. Being efficient in these areas helps a brand’s image for respecting user rights.
Aligning privacy compliance with information security practices
Privacy and security go hand in hand. A good framework should work with current security steps, like data tracking and breach plans. This way, sensitive data stays safe, no matter where it is.
Watching over data across borders is also key. Keeping data history clear and access tight helps avoid risks with global data. Security-first thinking lets businesses grow while staying up to date with global rules.
How to Implement a First-Party Data Strategy Across the Business
Switching to a first-party data strategy needs a clear plan. This plan should focus on business goals, not just new tech. It’s better to set goals that help your business grow over time.
Every tech choice should have a clear reason. This ensures that technology supports your business goals.
Start with business objectives and high-value customer journeys
First, find the customer journeys that are most valuable for your brand. Map these interactions to see where data is most important. Focus on moments where knowing more about the user improves your service.
It’s key to respond quickly to customer actions. Slow responses can make your data seem outdated. Prioritizing speed keeps your interactions timely and valuable.
Audit existing systems, permissions, and data flows
Before adding new tools, check your current data flows and setup. Find where data is stuck in silos and look at permissions. This audit shows where your data chain is broken, making it hard to see the whole user picture.
Look for missing identifiers that stop you from linking different interactions. A clear view of your setup shows security or compliance issues. Transparency in data handling is key to a lasting relationship with your audience.
Prioritize foundational capabilities before advanced personalization
Many businesses fail by trying complex automation first. You need to get the basics right. This includes good consent capture, accurate identity resolution, and consistent data quality.
Once your data is clean and consent is solid, you can grow your efforts. Start with closed-loop conversion tracking to check if your strategy works. By focusing on these basics, your move to personalization will be strong and effective.
Measuring the Return on Privacy-Centered Data Investments
Creating a strong measurement framework is key to turning privacy into a business strength. By linking your privacy-centered data to business results, you show it’s more than just a rule. It’s a way to grow.
Tracking data quality, consent rates, and audience match rates
Good data is the base of a solid plan. You need to check data quality like how complete and up-to-date it is. This ensures your insights are reliable.
Also, watching consent rates shows how well you’re valued by your audience. By looking at how well your data matches external platforms, you see its worth. Regular checks help spot and fix data collection issues early.
Measuring revenue, retention, and customer experience outcomes
It’s important to see how your data affects your profits. By linking your data to customer lifetime value, you find out which customers are most valuable. This shows if your personalization works.
Also, track how much more money you make from your own channels than from others. Better retention means happier customers. When customers trust you with their info, they stick around longer.
Evaluating risk reduction alongside financial performance
It’s crucial to balance making money with risk reduction. A good privacy setup means fewer data breaches. You can measure this by seeing how many records have clear purpose and consent.
Also, how fast and accurate you are with consumer rights requests matters. Keeping a clear data history protects you from legal trouble. Adding these security numbers to reports shows privacy is a priority for everyone.
Conclusion
First-party data is a strong asset for your business. It comes from direct connections with your customers. Using third-party data can be risky.
Having your own data makes your business more resilient. It helps you grow in a safer way.
To succeed, you need a system that connects data collection, consent, and rules. This system should also include security and identity checks. It makes sure your marketing works well while keeping user privacy safe.
Begin by setting up a solid system for your most important customer interactions. Start with simple, effective journeys. Then, you can move to more complex AI and personalization.
This step-by-step approach helps your team grow while keeping data safe. It’s a smart way to build your business.
Building trust with your customers is key in today’s digital world. Being open and responsible with data gives you an edge. Start checking how you handle data now to strengthen your brand’s future.